11 min read
TorchServe LPE: a fixed temp path, and a model server that trusts it
CVE-2026-123974: an attacker-controlled temporary directory can let a local user replace a model handler and execute code as the TorchServe service account.
christbowel
Software Security @ PAYONE GmbH
Turning attack surfaces into CVEs.
11 min read
CVE-2026-123974: an attacker-controlled temporary directory can let a local user replace a model handler and execute code as the TorchServe service account.
16 min read
A pre-auth reflected XSS in WordPress Core, patched in 7.0.3. Two sanitizers disagree about what a tag is, and a username walks through the gap. This is the breakdown: gdb on the PHP tokenizer, the real affected range (which every public writeup got wrong), the JS gadget the patch did not touch, and a detector.

21 min read
Five vulnerabilities in the Perspective analytics engine, including an unsandboxed eval() in the query path and a stored XSS in the plugin that loads by default. Chained, they take an attacker from writing one row of data to command execution on the server host.

20 min read
How two one-line oversights chain into code execution on 500 million sites

7 min read
How three copies of one G-code command revealed an out-of-bounds write reachable from a single serial line, confirmed on a real STM32 target.
17 min read
OWASP Dependency-Track ships a Portfolio ACL feature that promises multi-tenant isolation. Turns out it only blocks reads. A low-privileged user can suppress any vulnerability, rewrite triage decisions, poison audit trails, and inject rogue projects into another team's hierarchy. Here is how.
5 min read
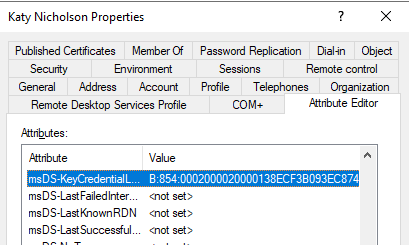
Shadow Credentials abuse msDS-KeyCredentialLink to authenticate as any user via PKINIT without touching their password. No reset, no ticket forging, no detection by most SOCs.