11 min read
TorchServe LPE: a fixed temp path, and a model server that trusts it
CVE-2026-123974: an attacker-controlled temporary directory can let a local user replace a model handler and execute code as the TorchServe service account.
Research notes, bug bounty writeups, reverse engineering and offensive security.
11 min read
CVE-2026-123974: an attacker-controlled temporary directory can let a local user replace a model handler and execute code as the TorchServe service account.
16 min read
A pre-auth reflected XSS in WordPress Core, patched in 7.0.3. Two sanitizers disagree about what a tag is, and a username walks through the gap. This is the breakdown: gdb on the PHP tokenizer, the real affected range (which every public writeup got wrong), the JS gadget the patch did not touch, and a detector.

21 min read
Five vulnerabilities in the Perspective analytics engine, including an unsandboxed eval() in the query path and a stored XSS in the plugin that loads by default. Chained, they take an attacker from writing one row of data to command execution on the server host.

20 min read
How two one-line oversights chain into code execution on 500 million sites

7 min read
How three copies of one G-code command revealed an out-of-bounds write reachable from a single serial line, confirmed on a real STM32 target.
17 min read
OWASP Dependency-Track ships a Portfolio ACL feature that promises multi-tenant isolation. Turns out it only blocks reads. A low-privileged user can suppress any vulnerability, rewrite triage decisions, poison audit trails, and inject rogue projects into another team's hierarchy. Here is how.
5 min read
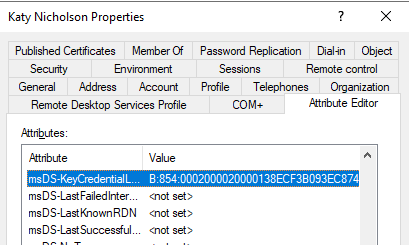
Shadow Credentials abuse msDS-KeyCredentialLink to authenticate as any user via PKINIT without touching their password. No reset, no ticket forging, no detection by most SOCs.

6 min read
ESC1 gets all the attention. The real kills happen through ESC9, ESC14, ESC15 and ESC16. These are the ADCS escalation paths that bypass modern hardening, abuse certificate mapping logic, and work even after KB5014754. Full chains, tooling, detection.

6 min read
Your Cobalt Strike beacon gets flagged in 30 seconds because your infrastructure is trash. This covers redirector chains, domain fronting alternatives, malleable C2 profiles, and the operational security that separates a red team from a pentest.
7 min read
Three kernel privilege escalation vulnerabilities in two weeks. All abuse page-cache corruption to overwrite read-only files in memory. No race condition required. Reliable root on every major distro. This is the technical breakdown and how to patch before you get hit.
7 min read
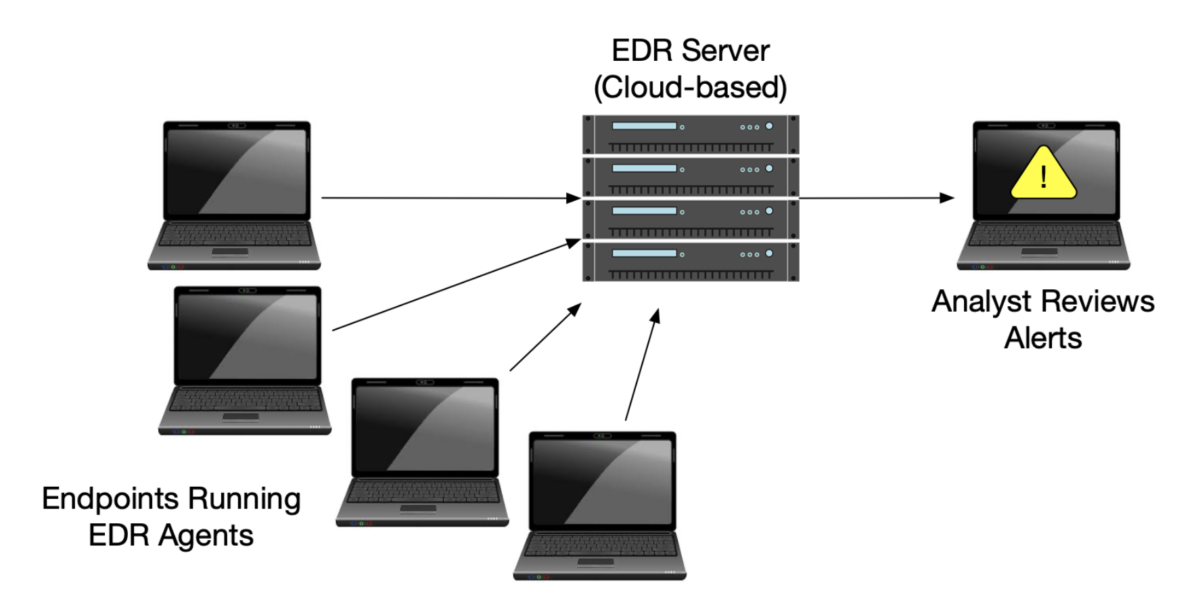
Every EDR hooks ntdll. Every EDR monitors ETW. Every EDR scans AMSI. This covers the techniques to bypass all three: direct/indirect syscalls, manual unhooking, ETW patching, AMSI manipulation, and the execution patterns that keep your implant alive.
7 min read
You have an IP. You need SYSTEM. This is the decision tree: what to check, what each misconfiguration gives you, where to go next. From network enumeration to domain compromise, every fork is covered.

7 min read
PsExec gets caught. WMI gets logged. RDP gets recorded. This covers the lateral movement techniques that APT groups actually use in long-duration operations: DCOM abuse, WinRM certificate auth, token manipulation, and persistence mechanisms that survive reimaging.

6 min read
Golden Tickets get caught. Silver Tickets have limitations. Diamond and Sapphire Tickets modify legitimate TGTs issued by the KDC, making them nearly invisible. Combined with DACL abuse chains, this is the current state of the art in AD persistence and escalation.
7 min read
Cloud security isn't 'someone else's problem.' Misconfigured IAM, exposed metadata, overprivileged service accounts. This is the decision tree for compromising AWS, Azure, and GCP environments: from initial access to data exfiltration.
30 min read
The complete methodology for auditing wireless networks. From WEP to WPA3, from WPS bruteforce to PMKID capture, from deauth to evil twin. Every protocol, every attack vector, every terminal output. The guide I wish existed when I started.
19 min read
Android Debug Bridge is a powerful developer tool. When left exposed on the internet, it becomes a root shell with zero authentication. This is the complete methodology: from recon to post-exploitation, and everything people forget to check.
12 min read
garak is the tool for scanning LLM vulnerabilities. Although the technique seems simple, it's not straightforward to use without drowning in noise. This article is a writeup of my deep dive into the project's internals.
5 min read
How a simple Host header manipulation poisoned Croogo's RSS feed and opened the door to phishing and domain spoofing.

8 min read
A deep dive into a timing attack vulnerability I discovered in Vendure's NativeAuthenticationStrategy.
3 min read
Understanding the mechanics of Kerberos tickets and how attackers crack service account passwords offline.
45 min read
Une collection massive de 60+ outils et ressources pour la défense, le monitoring et la réponse aux incidents (Blue Teaming).
75 min read
Analyse des techniques d'intrusion et de post-exploitation en environnement sécurisé.
No articles found.